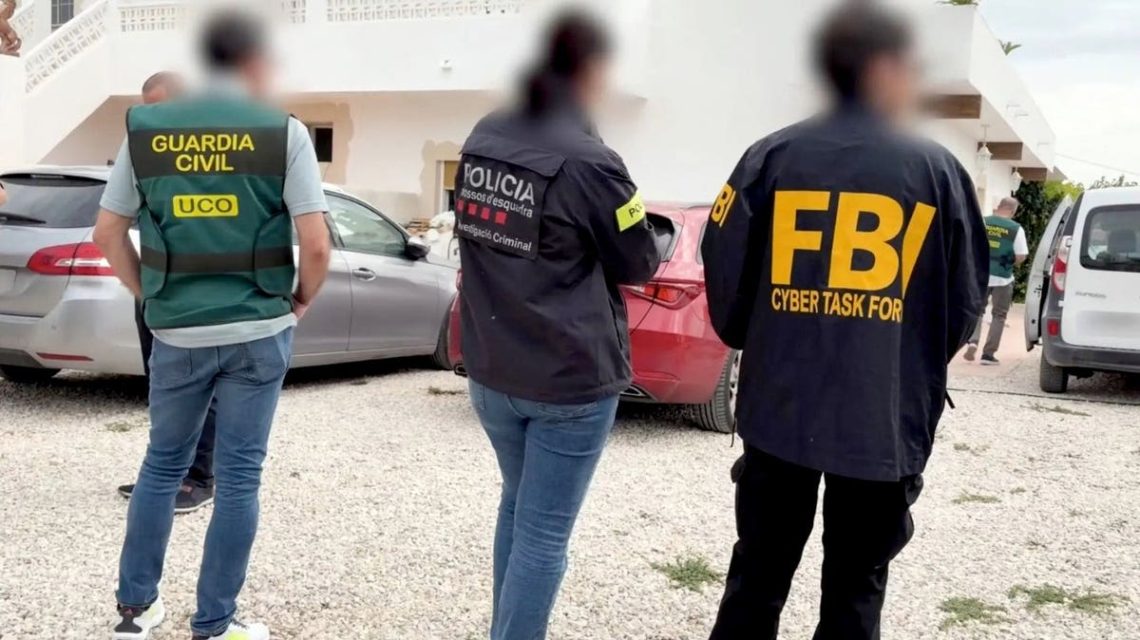
Picture the person at the helm of an international ransomware operation, and it’s unlikely a teenager comes to mind. Surprisingly, investigators have identified a 16-year-old as a key operator behind KillSec, a cybercrime group connected to approximately 1,000 suspected attacks globally. Of these, about 500 have been confirmed as successful. Recently, international law enforcement efforts have dismantled KillSec’s leak site and key servers, securing at least 110 terabytes of stolen data that could have been exposed or used against victims.
The takedown highlights the alarming accessibility of cybercrime today. Attackers continue to exploit vulnerable systems, turning stolen data into leverage. The investigation into KillSec revealed how the group operated, the role AI played, and measures to make such ransomware attacks more challenging to execute.
Coordination in the Operation KillSwitch
Known as Operation KillSwitch, coordinated action on September 30 involved agencies from the United States and several European countries. Europol and Eurojust facilitated the initiative. Law enforcement conducted eight searches across Greece, Romania, Spain, and the United Kingdom, arresting three suspects and seizing five central servers linked to KillSec’s operation. Authorities took control of the group’s dark web leak site used to name victims and demand ransom to prevent publishing stolen files.
The Teen Behind KillSec
The most striking aspect of the case is the involvement of a 16-year-old identified as KillSec’s suspected administrator. Another member, a developer, celebrated his 18th birthday in August, and may have been a minor during some alleged criminal activities. Investigators also identified individuals suspected of serving as negotiators and affiliates. Despite their age, KillSec’s activities were extensive. The group exploited software vulnerabilities and weak access points to infiltrate organizations and copy sensitive files.
Pressure on Victims
Once attacker obtained files, the pressure tactics began. KillSec allegedly threatened to publish stolen data using their dark web site if organizations refused to pay a ransom. Some files were reportedly disclosed when victims declined payment. Europol notes substantial ransom payments were received, illustrating the evolution of ransomware strategies. The stolen data itself can become a potent threat, causing significant damage even when backups are intact.
Utilizing AI for Attacks
Europol revealed members of KillSec used AI to support infrastructure and identify targets. AI assisted in speeding up operations without the need for deep technical knowledge previously required for such activities. Tools, stolen credentials, vulnerable systems, and AI assistance lower barriers, making cybercrime more accessible.
The Aftermath and Prevention
The investigation into KillSec remains active. Authorities examine seized computers, servers, and other evidence while tracing cryptocurrency and alleged criminal proceeds. New findings may reveal additional attacks, victims, or accomplices. Despite a major takedown, ransomware groups have a history of reshaping and resurfacing, underlining the necessity of preventive measures.
KillSec predominantly targeted organizations, not individual users. However, the methods underscore lessons for everyone. Exploiting software vulnerabilities and insecure access points remain prevalent threats. An old router, forgotten account, or unpatched computer can provide criminals an entryway. Compromised passwords offer the same risk.
Seven Security Habits to Minimize Ransomware Risks
- Install software and security updates: Regular updates fix known vulnerabilities. Enable automatic updates when feasible.
- Use strong, unique passwords: Avoid reusing passwords across different accounts. Utilize password managers for secure credential management.
- Enable two-factor authentication (2FA): Add extra authentication layers to critical accounts, utilizing secure methods like passkeys or security keys when available.
- Keep offline backups: Regularly back up vital data both on the cloud and external drives, ensuring drives are disconnected after backup.
- Be cautious with unexpected downloads: Do not open unsolicited files. Verify update prompts via applications directly.
- Deploy security software: Strong antivirus programs can detect threats. Keep software current and perform scans when systems act unexpectedly.
- Know the protocol if ransomware strikes: Disconnect infected devices from networks immediately. Avoid plugging in backup drives until systems are clean. Report incidents through the FBI’s Internet Crime Complaint Center (IC3.gov) or contact local FBI offices directly.
Ransomware attacks emphasize the importance of foundational security practices like updating devices, securing accounts beyond password protection, and maintaining backups. Vigilance in these areas can prevent attacks before they occur.
Questions remain about whether advanced hacking tools and AI are making cybercrime too accessible. Share your insights at Cyberguy.com, and sign up for the free CyberGuy Newsletter for tech advice, security alerts, and deals.
 Concerns Over Russia’s Biological Weapons Program
 Challenges and Opportunities in Data Center Development
 Concerns Arise Over ChatGPT for Teens
 Former OpenAI Researchers Challenge Dismissals
 AI and Human Connection: Hy’s Innovative Approach
 OpenAI Exposes Russian and Iranian Influence Operations Using AI